
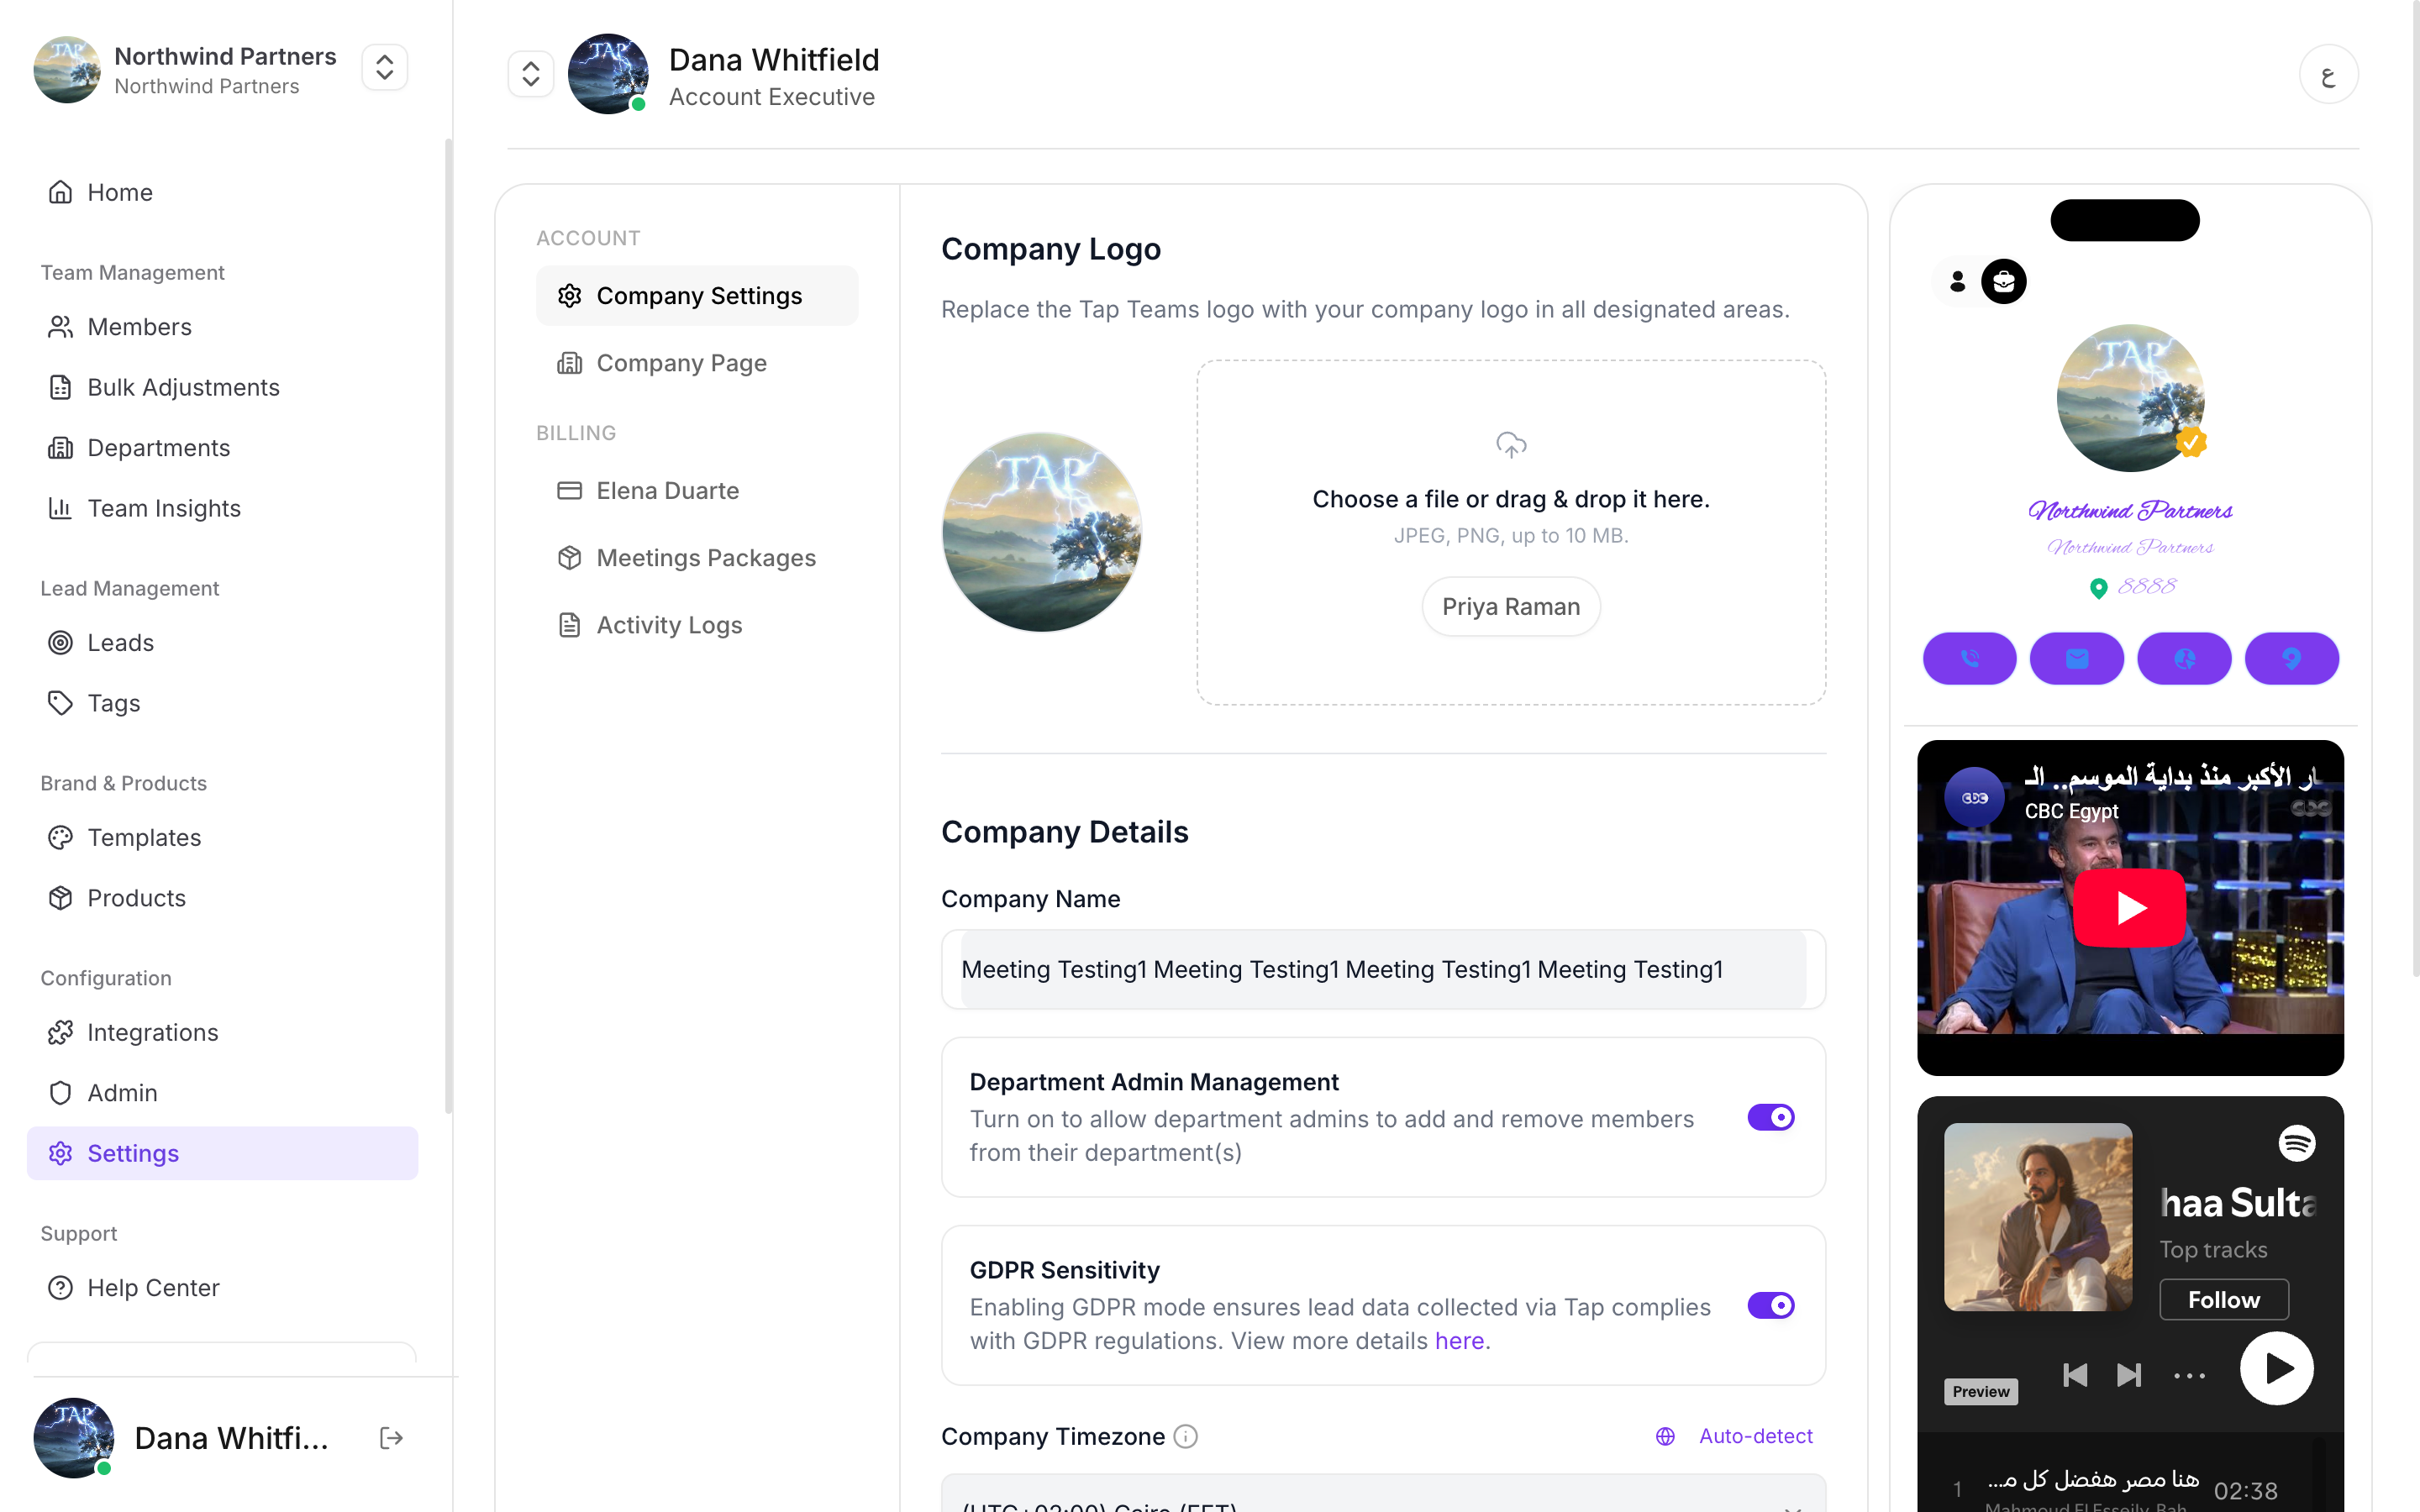
GDPR Sensitivity sits with the other company-wide switches
This is one switch inside a much larger obligation. Enabling it does not make your organisation compliant, and no software setting can. It supports your process; it doesn’t replace it.
What it changes
With GDPR mode on, visitors must give consent before their details are captured on your team’s public profiles, and that consent is stored with each lead.1
A consent box on the capture form
Every public profile’s capture form ends with a required checkbox, worded with your company’s name: “I agree to the collection and processing of my information by Acme in compliance with GDPR privacy regulations.” The form can’t be sent until it’s ticked.
2
Consent is recorded
Tap stores when consent was given, and which version of the notice the visitor saw.
3
You can see it on the lead
The lead’s page shows a Consent row — Given with the date — so you can answer “did they agree?” without digging.
The consent box is on the forms visitors fill in themselves. A lead a rep types in, scans from a business card, or imports from a file never saw that form, so it carries no consent record. Make sure you have a lawful basis for those another way.
Where your obligations actually sit
Whatever the setting does, these remain yours to handle:Lawful basis
You need a lawful basis for collecting each field. “It was useful” isn’t one — and every extra field on your capture form is another thing to justify.
Transparency
People must know who is collecting their data and why, at the point they give it.
Recording consent
Recording a conversation is separate from capturing contact details, and in many places needs its own explicit consent. Tell people before you start recording.
Erasure requests
You must be able to find and delete an individual’s data on request — including their meetings and transcripts, which deleting a lead doesn’t remove.
Handling an access request
When someone asks what you hold about them, find their lead and use Export → Download lead data. You get one file with their details, consent, notes, voice notes, meetings with transcripts, and enrichment results. See Managing leads.Handling an erasure request
1
Find every record for that person
Search Leads by name and by email. The same person captured at two events with two different addresses is two records.
2
Delete the leads
Deleting a lead also deletes its notes, voice recordings, and enrichment data. Its meetings are kept, no longer attached to the lead.
3
Ask us to erase their meetings
If the person was recorded, contact support to have those meetings and their transcripts erased.
4
Delete from your CRM too
Records already synced live in your CRM independently. Deleting in Tap does not remove them from HubSpot, Salesforce, or anywhere else.
5
Check your other destinations
If you route leads through Zapier, the data has also reached whatever that Zap feeds — spreadsheets, Slack, email tools. Those are part of your footprint too.
Practical steps that reduce your exposure
Collect fewer fields
Collect fewer fields
The single most effective privacy measure available to you. Data you never collected needs no lawful basis, no storage, and no deletion.
Say what you're doing, out loud
Say what you're doing, out loud
“I’ll pop you into our system and someone will follow up next week” takes three seconds and covers transparency far better than fine print nobody reads.
Ask before recording, every time
Ask before recording, every time
Not once at the start of the day. Each conversation.
Keep your destination list current
Keep your destination list current
Know every place captured data ends up. You can’t honour an erasure request against a system you forgot exists.
This page describes product behavior, not legal advice. Talk to your own advisors about what your organisation needs to do.